Professional work · Principal AI Engineer at HRMLESS · 2026
Giving AI agents safe access to real company systems
HRMLESS is an HR technology company. Its AI needed to reach internal systems safely, and its customers needed proof that the setup was secure and fair. I owned that work from requirements and architecture through deployment and troubleshooting in production.
What I built
This was my job, so the code, architecture, and audit evidence belong to HRMLESS. Here's the kind of system I built and how I went about it.
- Model Context Protocol (MCP) services in Python with FastAPI and FastMCP. They gave AI agents access to internal systems through role-based authorization, scoped tokens, and audit logging, so every agent action had limits and a record.
- Single sign-on with Keycloak federated to Microsoft Entra ID, and credentials kept in HashiCorp Vault instead of config files.
- The platform underneath: Kubernetes (RKE2), PostgreSQL, Redis, and observability tooling, which I set up and kept running.
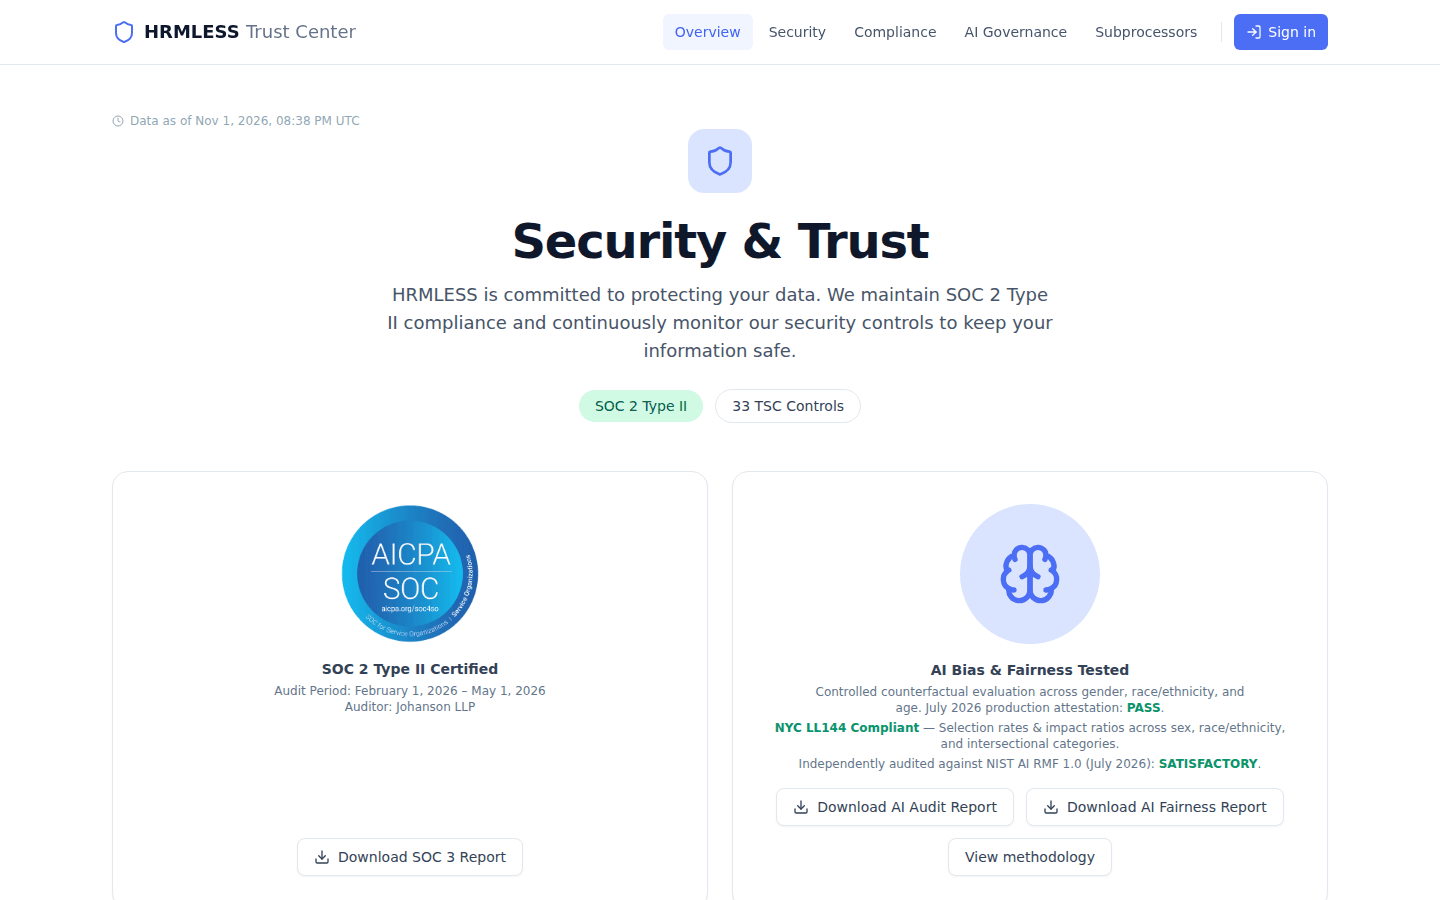
- An integration between the Probo compliance platform and the customer-facing Trust Center, so published security information came from the system of record instead of manual updates.
- Python scripts that pulled audit evidence from source systems through their APIs, replacing manual collection before each review.
- SOC 2 Type II readiness and the audit itself, plus the design of the company's AI governance program.
Worth knowing
Security and governance weren't a separate phase bolted on at the end. They were part of how the systems got built, which is a big reason the audits went smoothly.
I used Claude and Cursor to speed up development. I was the one accountable for what shipped and for fixing it when it broke.