Professional work · Principal AI Engineer at HRMLESS · 2026
Giving AI agents safe access to real company systems
HRMLESS is an HR technology company. Its AI needed to reach internal systems safely, and its customers needed proof that the setup was secure and fair. I owned that work from requirements and architecture through deployment and troubleshooting in production.
What I did
- Built MCP services in Python that let AI agents use internal systems, with role-based permissions, scoped tokens, and an audit trail.
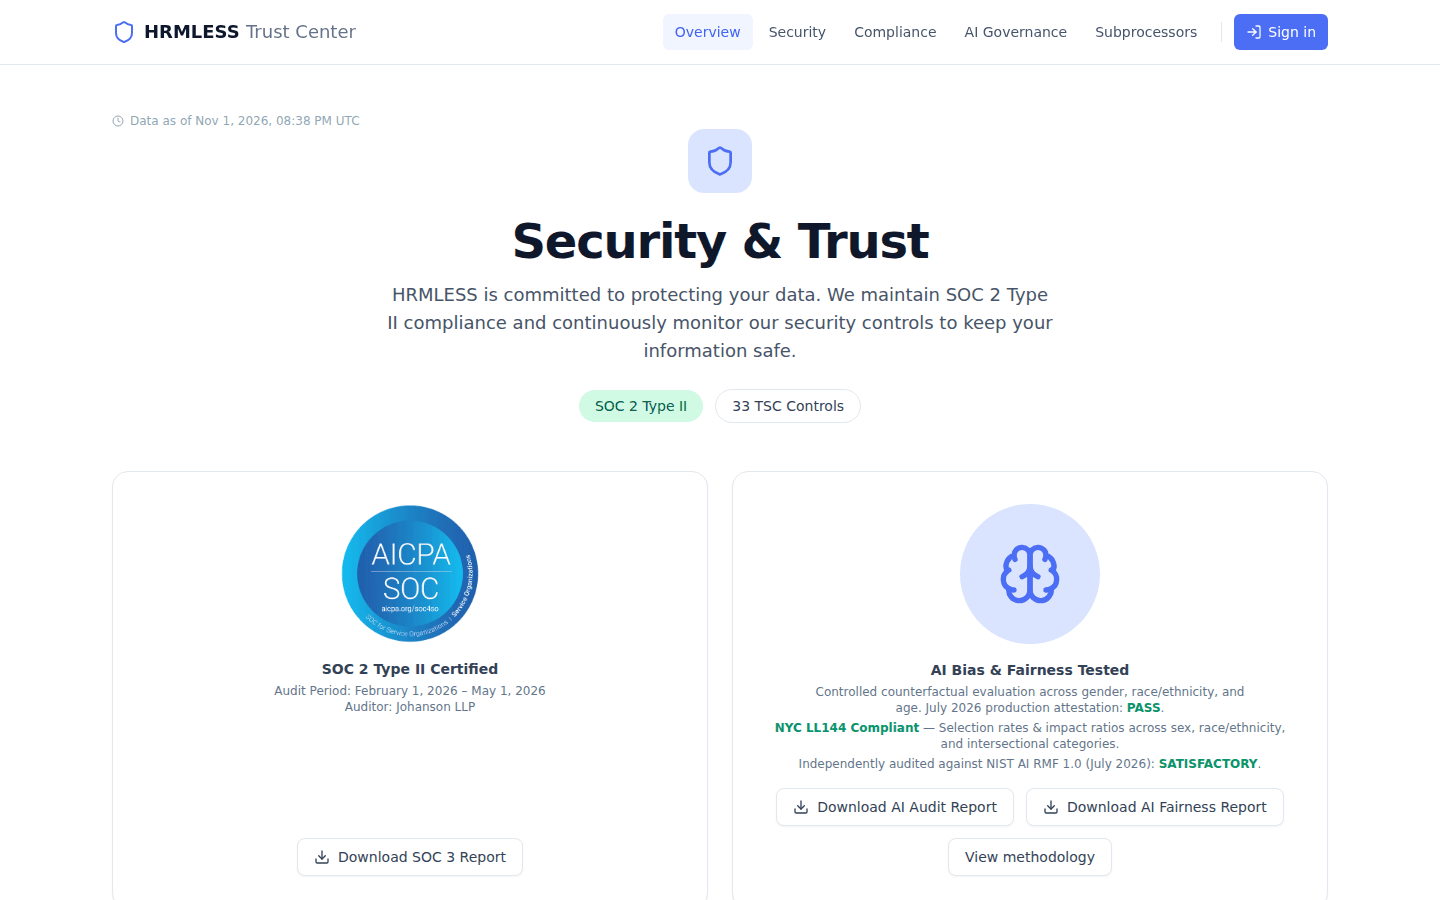
- Connected the compliance platform to the public Trust Center, so what customers see comes straight from the system of record.
- Automated audit evidence collection with Python, so nobody had to gather it by hand before every review.
Result: I led the SOC 2 Type II audit across 33 controls to a clean report, and the AI governance program I designed was rated Satisfactory in an independent NIST AI RMF 1.0 assessment in July 2026.
Also: single sign-on with Keycloak and Entra ID, secrets in Vault, Kubernetes, PostgreSQL, Redis, and observability tooling. The code and architecture stay with the company.